William F. Leach Jr. Resume & CV

CISO · Cyber assurance · Author

William F. Leach Jr.

I build security programs that can prove they work.

Former bank CISO and CIO, healthcare CISO, managed security vice president and U.S. Navy information assurance manager. Author of The Assurance Gap.

  • CISSP since 2004
  • 20-year U.S. Navy career
  • Held Top Secret clearance
  • Baton Rouge, Louisiana
Portrait of William F. Leach Jr.
Cybersecurity executive
security risk assessments led
1,000+
to HITRUST CSF certification, built from scratch
11months
managed security practice built, 500+ MSP clients
$3.4M
fewer critical vulnerabilities at a publicly traded bank
90%
Navy Reserve centers under my information assurance
600+
of U.S. Navy service, retired as a commanding officer
20years

Profile

Security leadership that shows its work

My work comes down to one question: can the organization prove that its controls work? I have answered it for bank examiners, auditors, insurers and boards.

At First Guaranty Bancshares I built the information security program under FDIC and FFIEC examination and was promoted from CISO to CIO within four months. At eQHealth Solutions I took the company to HITRUST CSF certification in 11 months. At Lockstep Technology Group I built two security operations centers and a $3.4M managed security practice. In the Navy I was the information assurance manager for more than 600 reserve centers.

Today I serve clients as a virtual CISO through Transformyx Technology Services and lead cybersecurity, network and infrastructure work at OneVision Consulting, including NIST-based risk frameworks for chemical manufacturing. My book, The Assurance Gap, defines the independent Cyber Assurance Officer.

  • Board and executive reportingRisk, evidence and cost, stated in business terms.
  • Examination and audit readinessFFIEC, HIPAA and HITRUST, CMMC, PCI DSS and SOC 2.
  • Security operations from zeroSOCs, vulnerability management, penetration testing and incident response.
  • Budgets and teamsIT budgets to $8.2M and cross-functional teams of 400+.

Now

  • Principal & Virtual CISO, Transformyx Technology Services
  • Managing Director, OneVision Consulting
  • Finishing the CyberCAAT demo
Career

The record, 2002 to today

Security and technology leadership across banking, healthcare, managed security services and the U.S. Navy.

Roles by organization, 2002 to 2026

Hover over or tab to a bar for the title and dates.

Transformyx Technology Services logo

Transformyx Technology Services, LLC

Independent cybersecurity advisory practice

Current

Principal & Virtual CISOJan 2024 – Present

  • Virtual CISO leadership, risk assessments and independent cyber assurance for small and mid-sized organizations, aligned to NIST CSF 2.0, NIST SP 800-171, CMMC, ISO/IEC 27001, HIPAA and PCI DSS.
  • Risk assessments with gap analysis, corrective action plans and 12-month remediation roadmaps; policy architecture, tabletop exercises and attack-surface analysis.
  • Designed and built the CyberCAAT cyber-GRC platform and wrote The Assurance Gap.
OneVision Consulting logo

OneVision Consulting, LLC

Strategic consulting firm

Current

Managing Director of Cybersecurity, Network and InfrastructureMar 2024 – Present

  • Leads cybersecurity, network and infrastructure services for industrial clients: vCISO services, risk assessments, compliance consulting and IT advisory.
  • Implemented NIST-based risk frameworks for ICS/OT environments under DHS and U.S. Coast Guard requirements for critical infrastructure.
  • Ran vulnerability assessments and set incident response protocols for chemical manufacturing operations.
First Guaranty Bank logo

First Guaranty Bancshares, Inc.

Publicly traded bank holding company

SVP, Chief Information Security Officer and Chief Information OfficerMar 2022 – Nov 2023

  • Promoted from CISO to CIO within four months; rated Distinguished, the bank’s highest performance rating, in the final annual review.
  • Built the Information Security Program under FDIC/FFIEC guidance; kept 840 endpoints at 100% compliance and cut critical vulnerabilities 90% and phishing incidents 70%.
  • As CIO, led a 27-person IT organization on an $8.2M budget; automated 50+ processes and cut service desk response times 87%.
Lockstep Technology Group logo

Lockstep Technology Group

Managed security services provider, formerly Transformyx

Vice President of CybersecurityOct 2017 – Mar 2022

  • Grew the managed security practice to $3.4M in revenue serving 500+ MSP clients; built and led two security operations centers.
  • Oversaw 1,000+ risk assessments and 50+ penetration tests; launched vCISO services and penetration testing as a service.
  • Automated compliance evidence for 500+ clients’ HITRUST and SOC 2 programs, cutting compliance effort 70%.
eQHealth Solutions logo

eQHealth Solutions

Healthcare quality-improvement organization, now part of Acentra Health

Chief Information Security Officer, Executive DirectorApr 2015 – Oct 2017

  • Built the security program from inception and achieved HITRUST CSF certification in 11 months, addressing 700+ controls.
  • Architected the automated GRC framework that sustained HITRUST CSF and SOC 2 Type II compliance across 900+ controls.

Executive Director, Project Management OfficeSep 2013 – Apr 2015

  • Founded the IT PMO (21 staff, four development squads), improving project performance 300%.
Amedisys logo

Amedisys, Inc.

Home health and hospice provider, now part of Optum

Director, Strategic IT Sourcing and ProcurementDec 2011 – Sep 2013

  • Led IT sourcing, vendor risk management and procurement for a $110M+ contract portfolio; saved $4M+ through contract optimization.
  • Ran 8 competitive RFPs and negotiated $12M+ in contracts.
Transformyx logo

Transformyx

IT and managed services provider, now Lockstep Technology Group

Vice President of OperationsOct 2006 – Sep 2011

  • Directed operations and a 17-person team; delivered infrastructure upgrades with zero outages.
  • Led $2.4M in USAC E-rate contracts for 14 schools; taught CISSP, CEH, CISM and CompTIA certification courses.

Education

Two master’s degrees on a business foundation

Regis University logo

Master of Science

Cybersecurity and Information Assurance

Regis University

Denver, Colorado

regis.edu
Southeastern Louisiana University logo

Master of Science

Data Science and Applied Technology

Southeastern Louisiana University

Hammond, Louisiana

southeastern.edu
Auburn University logo

Bachelor of Science

Business Administration, Management Information Systems

Auburn University

Auburn, Alabama · commissioned a U.S. Navy officer here in 1996

auburn.edu

University programs I delivered

  • Louisiana State UniversityBuilt a NIST SP 800-171 program and delivered security training for end users.
  • Tulane UniversityDelivered end-user training and system test and evaluation for certification and accreditation.

Credentials

Eight certifications, CISSP since 2004

  • CISSPCertified Information Systems Security ProfessionalISC2 · since 2004
  • CRISCCertified in Risk and Information Systems ControlISACA
  • CGEITCertified in the Governance of Enterprise ITISACA
  • PMPProject Management ProfessionalProject Management Institute
  • CEHCertified Ethical HackerEC-Council
  • CCSFPCertified CSF PractitionerHITRUST
  • CMMC CCPCertified CMMC ProfessionalThe Cyber AB
  • CSMCertified ScrumMasterScrum Alliance

Frameworks and regulations

  • NIST CSF 2.0
  • NIST SP 800-53
  • NIST SP 800-171
  • CMMC 2.0
  • ISO/IEC 27001:2022
  • CIS Controls v8.1
  • HITRUST CSF
  • HIPAA
  • FFIEC
  • GLBA and Regulation P
  • SOX
  • PCI DSS
  • SOC 2
  • GDPR
  • FISMA
  • MITRE ATT&CK
  • NIST AI RMF
  • ISA/IEC 62443

Sectors

Banking and financial services · Healthcare · Chemical manufacturing and critical infrastructure · Defense and government · Managed security services · Education · Automotive

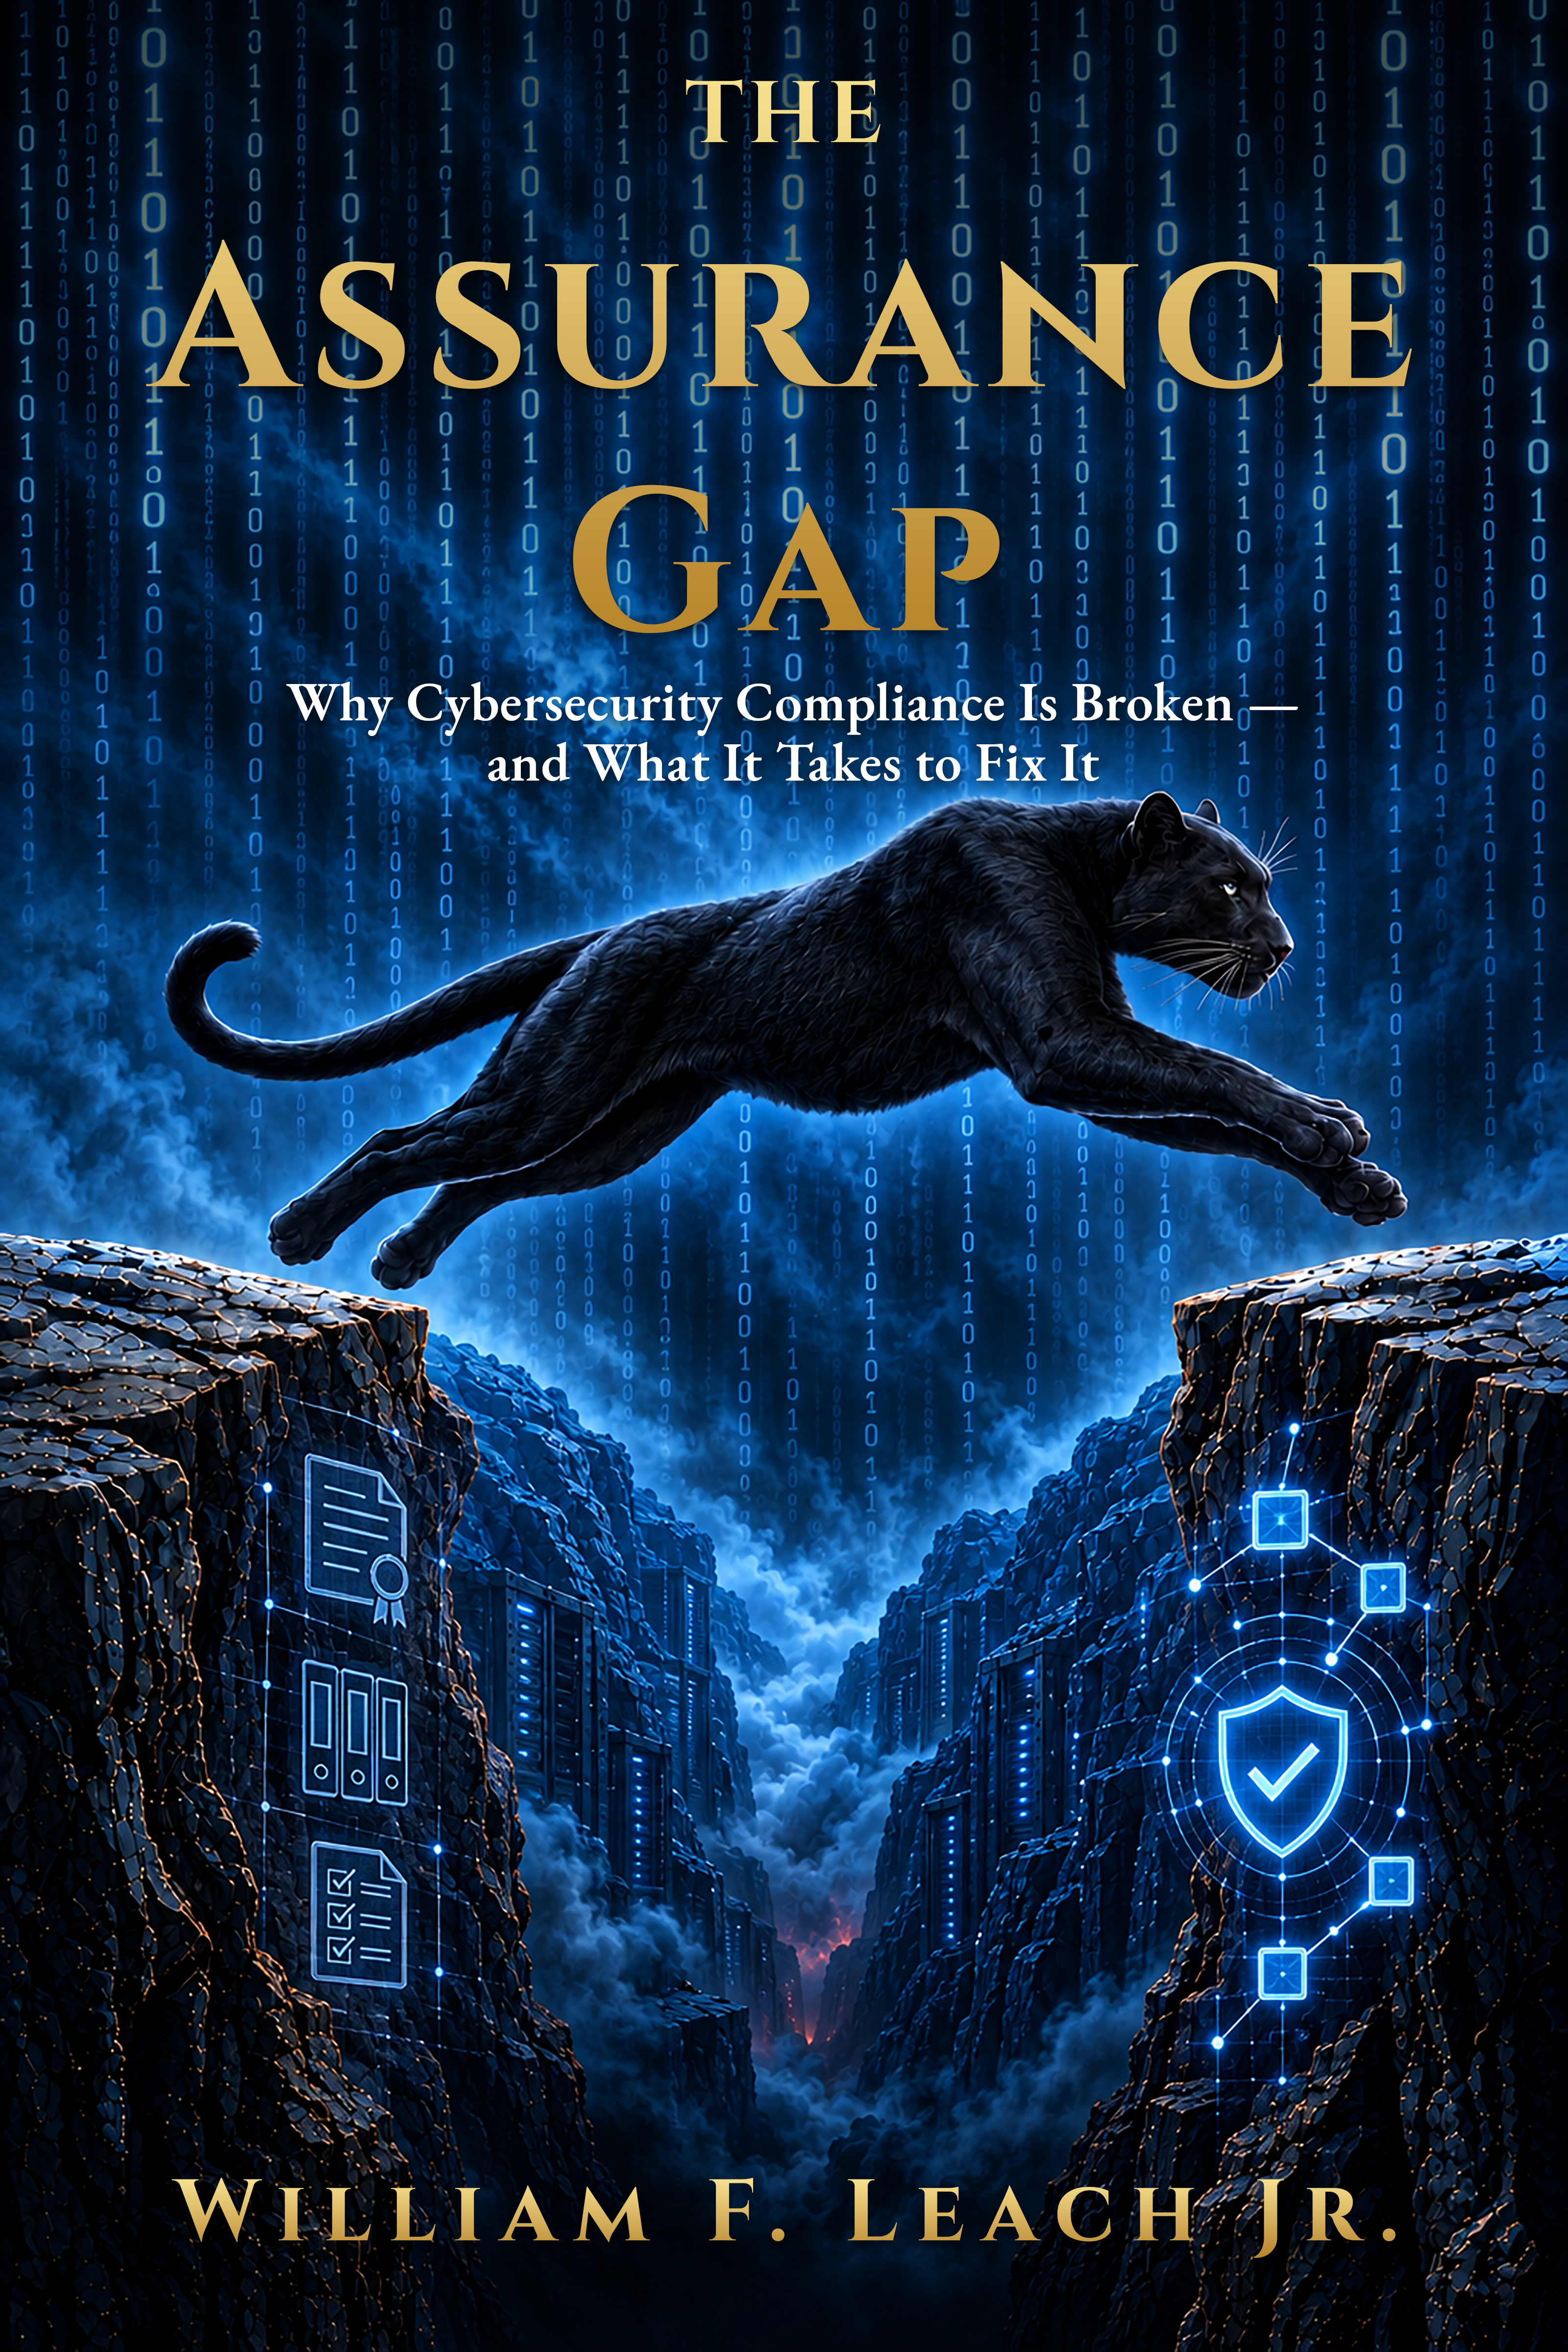
Cover of The Assurance Gap by William F. Leach Jr.
Buy on Amazon

Paperback · ISBN 979-8-234-24281-5
Kindle edition

The book

The Assurance Gap

Why Cybersecurity Compliance Is Broken — and What It Takes to Fix It

Organizations pass their audits, hold their certifications and sign their insurance attestations, and they are breached anyway. The Assurance Gap argues that the costliest failure in cybersecurity is the absence of independent verification. Finance separates the people who keep the books from the people who audit them. Cybersecurity often lets the same providers operate the controls and vouch for them.

Drawing on enforcement actions, court cases, insurance disputes and the Pentagon’s own lessons, the book sets out the fix: six pillars of cyber assurance, continuous evidence in place of annual attestation, an independent Cyber Assurance Officer, and a program that begins with a 90-day assessment.

The expensive day is not the day of the breach. It is the day an examiner, an insurer, or a plaintiff’s lawyer compares what was attested with what was running.

From About This Book
  • Transformyx Technology Services, 2026
  • 21 chapters, about 350 pages
  • For executives, boards and security leaders

The six pillars of cyber assurance

Controls in each pillar, 202 in all (Part IV of the book)

In development: The Assurance Gap Executive Workbook, with a worksheet for each chapter’s closing question, the six pillars as a self-assessment and a dated 90-day checklist.

Platform

CyberCAAT™

The cyber-GRC platform I designed and built to put the book’s method to work: evidence comes in from the tools a company already runs, is tested against one control catalog, and goes out as a posture score and executive reports.

Evidence in

Operating data

Endpoint, vulnerability and IT operations data from SentinelOne, Rapid7 and ManageEngine.

Tested in

CyberCAAT

17control domains
113scheduled control processes

One harmonized control catalog drawn from nine authoritative sources.

Mapped to

Frameworks

  • NIST CSF 2.0
  • ISO/IEC 27001:2022
  • CIS Controls v8.1
  • NIST AI RMF
  • ISA/IEC 62443
  • CMMC 2.0

Reported as

Posture score

Scored on a 200 to 850 scale, with risk assessments, vulnerability tracking and executive reports.

Built in C#, .NET 8, Blazor and Azure SQL. A demo is in progress. tfmxts.com/cybercaat

Speaking

Talks for security, audit and board audiences

Available for conference sessions, chapter meetings and board briefings.

Security and audit conferences

Grading Your Own Homework: The Conflict at the Heart of Managed Security

When one provider operates the controls, monitors them and vouches for them, findings come back clean without anyone lying. How the conflict works, why insurers deny claims over it, and how an independent assurance function fixes it without new tools.

ISACA, IIA and ISC2 chapters

Audit Day and the Other 364: From Point-in-Time Compliance to Continuous Assurance

An audit certifies what was true on one day, and controls drift afterward. How to test the gap between attested and operating controls with evidence dated when each control ran, verifiers independent of operators and an assurance calendar.

Boards and executive teams

What You’ve Signed: A Briefing on the Assurance Gap

The representations your organization has already made, three questions that test them, and a 90-day start: an owner, dated evidence for three controls and a board-level report.

Bio for programs and introductions

William F. Leach Jr. is a cybersecurity executive and practicing virtual CISO with more than 26 years in cybersecurity and information assurance. He has served as CISO and CIO of a publicly traded bank, CISO of a healthcare quality-improvement organization, VP of Cybersecurity at a national MSSP, and Information Assurance Manager for 600+ Navy Reserve centers. He founded Transformyx Technology Services and wrote The Assurance Gap (2026), which introduces the Cyber Assurance Officer.

Documents

Resume and curriculum vitae

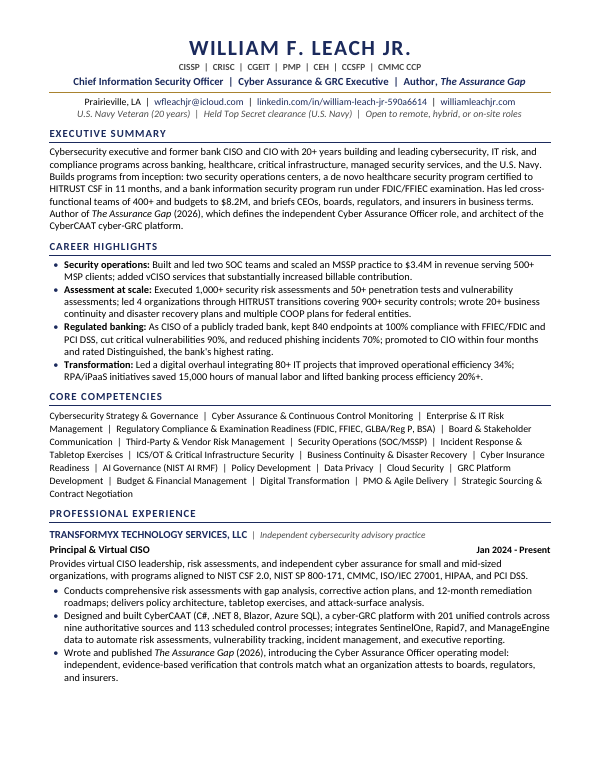
First page of the resume

Resume

PDF · 3 pages · September 2026

Leadership roles, measured results, credentials and education.

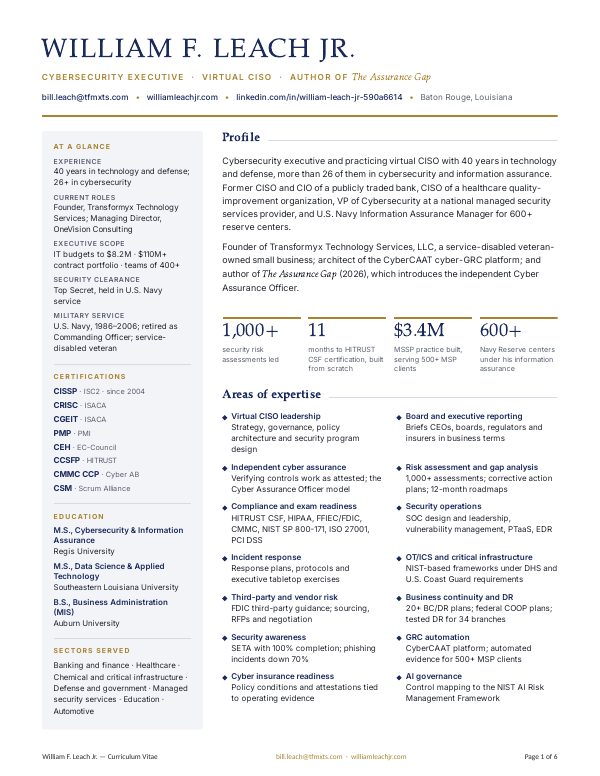
First page of the curriculum vitae

Curriculum vitae

PDF · 6 pages · September 2026

The full record for proposals and panels: engagements, publications, teaching, frameworks and firm details.

Phone number available on request.

Contact

Leadership roles, briefings and talks

For leadership roles, board briefings, speaking or the book, email is the best way to reach me.